 By Addison Thompson
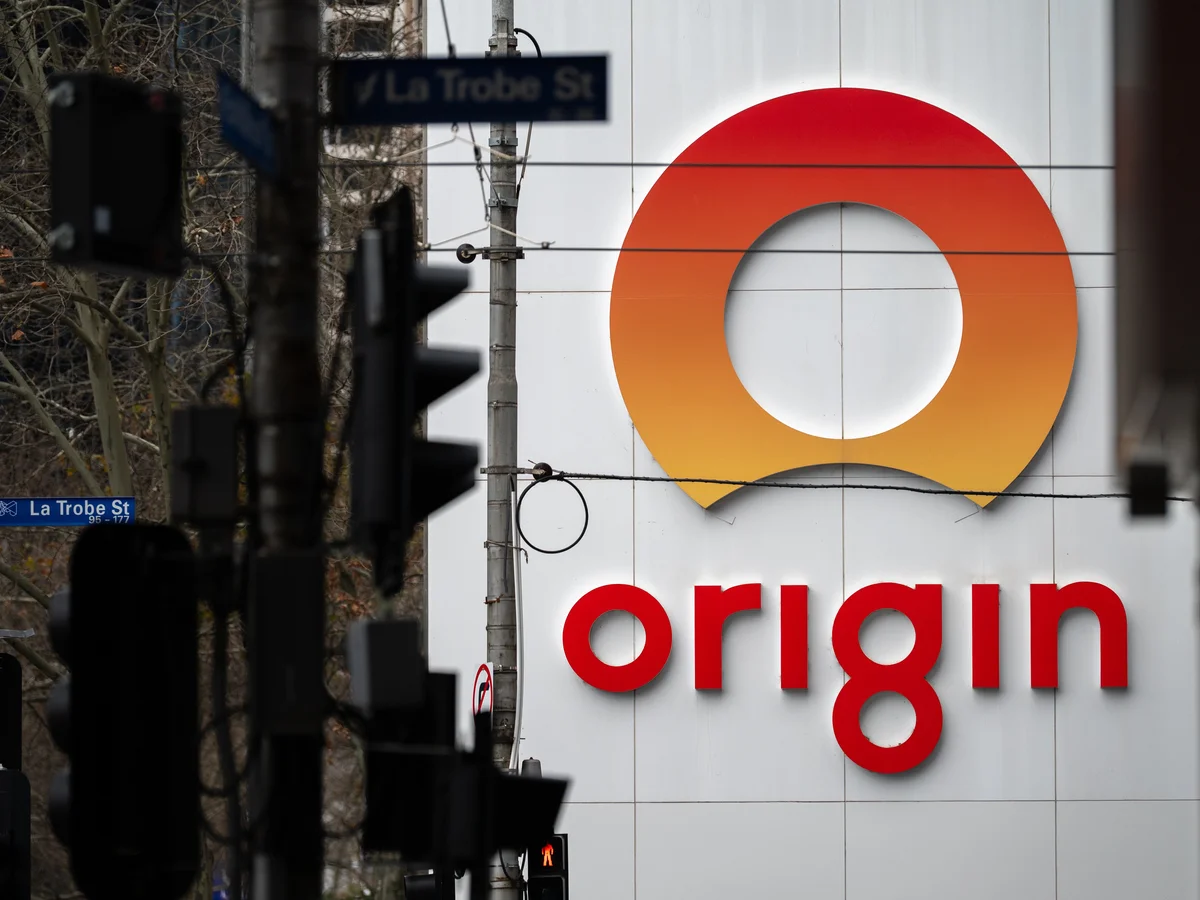
Origin Energy, Australia’s largest electricity and gas retailer, told the market on July 28, 2026 that about 900,000 current and former customers had personal information accessed in a data breach — a figure it reached five days after first confirming an intrusion, and roughly three weeks after it had looked at an early warning and decided the threat was not credible.
The incident has become one of the most closely watched Australian breaches since Optus and Medibank in 2022, less for its raw size than for two features: the company’s initial dismissal of the warning, and the fact that investigators traced the compromise to a former employee at an offshore call center run by a contractor.
A threat dismissed, then confirmed
Origin’s own incident page sets out the timeline. In early July 2026 the company became aware of what it describes as a potential security threat, which it did not at the time consider credible. On July 22, new information emerged indicating a possible incident — the same day The Australian reported that an alleged hacker had contacted the paper with a sample of customer records. Origin confirmed unauthorized access to customer data on July 23, and put a number on it on July 28.
According to ABC News, the person claiming responsibility sent the paper a sample of 50 customer records and later contacted the ABC directly, supplying what they said were internal Origin screenshots. Origin serves more than 4.7 million customers, so the confirmed figure covers roughly a fifth of its base.
Chief executive Frank Calabria apologized publicly. “To our customers, I am sorry,” he said. “We don’t take for granted the trust customers place in Origin and our safeguarding of their information.”
What was actually accessed
Origin spent three weeks working out, customer by customer, what had been taken. On August 21 it said that review was substantially complete. The breakdown it published is unusually granular for an Australian disclosure:
- For most of the 900,000 affected people: name, address, date of birth, contact phone number, account information, and either the last four digits of a credit card or the last three digits of a bank account.
- Around 15,000 customers: government concession scheme or program numbers.
- Around 100 customers: identity document numbers.
- Around 60 customers: full bank account numbers.
Origin stated that “incomplete credit card or bank account information cannot be used to make purchases or access accounts.” That framing matters, because the company had earlier told the Australian Securities Exchange that no financial details were involved — a position it subsequently revised. As of the August update, Origin said the attacker had not published or leaked the data.
The Manila connection
On August 18, the ABC reported that authorities had traced the compromise to a former employee of Accenture in Manila, who allegedly sought to extort Origin for the return of the data. Accenture operates offshore contact centers for Origin, including the Manila site where the suspect had worked.
Accenture declined to engage with the substance. “It is not appropriate for us to comment on Origin’s data security incident, which we understand remains under active investigation,” a spokesperson told the ABC. The Australian Federal Police said its investigators were “focused on gathering evidence, identifying those responsible, and disrupting any associated criminal activity.”
That detail moves the story out of the usual ransomware-gang frame and into third-party and insider risk — a category Australian regulators have been pressing on for several years, and one that outsourced customer service arrangements sit squarely inside. It is also the part of the incident Origin has said least about, citing the live criminal investigation.
Regulators, police and the bill
Origin says it is working with the Australian Cyber Security Centre, the National Office of Cyber Security, the Australian Federal Police and the Office of the Australian Information Commissioner (OAIC). The OAIC administers the Notifiable Data Breaches scheme, under which organizations covered by the Privacy Act must notify the regulator and affected individuals about eligible breaches likely to cause serious harm.
The regulator has not announced an enforcement outcome, and none should be assumed: OAIC assessments of large breaches routinely run for a year or more, and the Optus and Medibank matters both went to Federal Court proceedings well after the initial disclosure. What is on the record so far is remediation, not penalty.
Origin is offering affected customers a free 12-month subscription to Equifax Protect credit monitoring, plus access to IDCARE, Australia’s not-for-profit identity and cyber support service. It extended customer support hours and set up a dedicated contact line. The company has not disclosed a financial cost estimate for the incident.
What other organizations are drawing from it
Three points from the public record are being repeated by Australian security practitioners in the weeks since.
The first is about triage. An early warning that is assessed as not credible still needs a documented basis and a route back to reassessment. Origin’s own timeline shows a three-week gap between the initial signal and confirmation, and that gap is the single most quoted element of the incident.
The second is about scope of third-party access. Contact center staff — whether employed directly, by a contractor, or offshore — frequently need broad read access to customer records to do the job. Whether that access is time-bounded, logged, and monitored for bulk retrieval is a governance question, not a technical one, and it is the question the Accenture link puts on the table.
The third is about disclosure discipline. Origin’s public position on whether financial data was involved changed between its first ASX statement and its later customer notifications. Speaking early is expected under the Notifiable Data Breaches scheme; speaking with more certainty than the forensics support is what generates the second news cycle.
UNSW cybersecurity researcher Richard Buckland, quoted by the ABC, framed the human side plainly, calling 900,000 affected people “a lot of human suffering” and noting the incident could have reached considerably further. For customers, the practical advice from Origin and IDCARE has been conventional and unglamorous: watch for unexpected contact referencing account details, treat unsolicited calls claiming to be from the retailer with suspicion, and take up the credit monitoring on offer.
Sources
- Cyber incident update — Origin Energy
- Origin Energy believes 900,000 customers’ data accessed in breach — ABC News
- Origin Energy hack traced to Accenture’s Manila call centre — ABC News
- Dozens of Origin Energy customers’ full bank details, ID numbers accessed in July breach — ABC News
- Notifiable Data Breaches scheme — OAIC